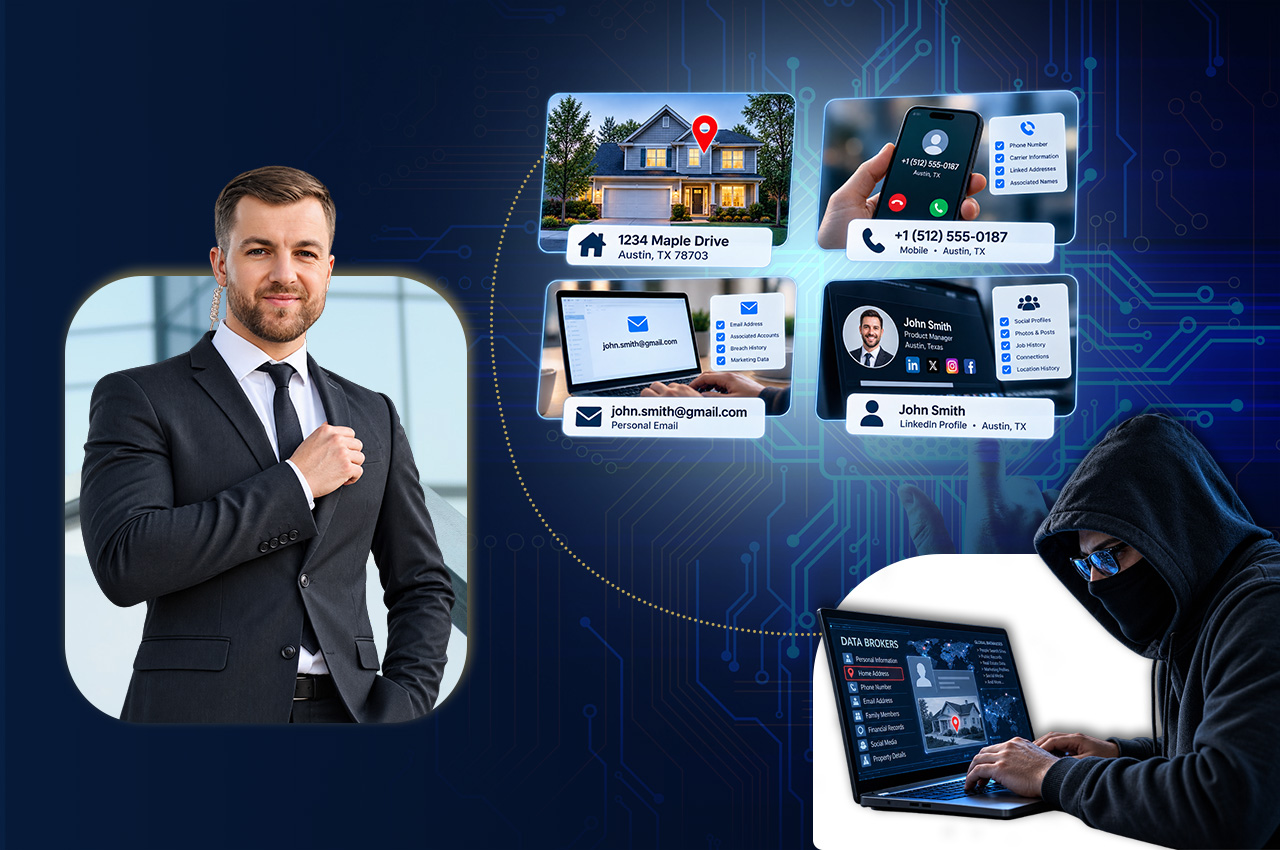
Ask most executives whether their home address is public and they will say no. They have never posted it. The company doesn’t list it. An assistant screens the mail. Then someone types their name into a people-search site, and the address comes back in under a minute, along with a spouse’s name, the children’s names, an old cell number and a map pin dropped on the front door.
That gap between what an executive believes is private and what is actually for sale is where a lot of modern threats begin. The person who turns up at a CEO’s driveway after a layoff announcement or a viral controversy rarely did any real research. Most of the time, they paid a few dollars.
Here is how that address gets out, and why it keeps coming back after you think it’s gone.
It starts with records nobody meant to publish
Data brokers don’t usually hack anything. They collect. Most of the raw material is public or close to it: property deeds and tax assessor files, voter records in states that sell them, court filings, business registrations, professional licenses and change-of-address data.
Property records do the most damage. When an executive buys a home in their own name, the county records the deed, and many clerk and assessor portals let anyone search by owner. In New York City, deed records are searchable online. On Long Island and across Florida, county clerk and property appraiser sites work in much the same way. Nobody has to guess. The house is tied to the name in an official record.
Business filings add another layer. An executive who once served as an officer, director or registered agent of an LLC may still have a home address sitting in a state corporate database, left over from a filing made years before anyone thought about it.
Commercial data fills in the rest
Public records give a broker the address. Commercial sources give them the context that makes it useful to someone with bad intentions.
Brokers buy and trade marketing lists, loyalty-program data, subscription records, warranty registrations, app data and files from other brokers. Each source holds a fragment. One has a name and a phone number, another has an email and a ZIP code. Matching software joins the fragments into a single profile, and that profile is what people-search sites sell.
For an executive, the most dangerous part is often the “relatives” section. It points to an adult child’s apartment, an elderly parent’s house or a vacation property, and none of those places have any security at all.
Why the address comes back after you remove it
Plenty of executives, or their assistants, have been through a round of opt-outs. It feels finished. Six months later the same address is back. There are a few reasons for that:
- Brokers resell to each other.Removing a listing from one site does nothing about the copy another broker bought last year.
- The public record never changed.If the deed is still in the executive’s name, the next data refresh pulls it straight back in.
- New activity creates new records.A refinance, a vehicle registration or a new utility account can quietly re-seed the profile.
- Opt-outs are site by site.One request covers one listing on one website, and there are hundreds of these websites.
California residents now have a stronger tool. Under the state’s Delete Act, the DROP platform lets a Californian send one deletion request to every registered data broker, and brokers had to begin processing those requests on August 1, 2026. An executive living in Manhattan, Westchester, Nassau County or Palm Beach has no equivalent option. For them, removal is still manual, and it never really ends.
What an exposed address actually enables
It is easy to file this under privacy annoyances. In protective work, we treat it as the first step of an attack cycle.
Someone angry about a business decision needs to know where to go. Someone planning a burglary wants to know when the family travels. A fraudster trying to talk their way past a bank or an executive assistant needs just enough personal detail to sound believable. A home address, the names of relatives and a phone number cover all three.
Physical and digital exposure feed each other, too. The same profile that reveals the address often lists personal email accounts, and those become targets for phishing aimed at family devices that corporate IT never touches. Delta has investigated targeted spear-phishing campaigns against senior leaders, and the groundwork behind that kind of attack usually starts with exactly this sort of freely available detail.
Reducing exposure is a program, not a cleanup
The executives who stay off these sites don’t get there with one sweep. What works looks more like maintenance:
- Map the footprint first.Find out what is actually out there across people-search sites, property records, corporate filings and the social media accounts of family members.
- Fix the source where you can.Future property purchases can be structured through a trust or LLC on counsel’s advice, and business filings can use a registered agent address instead of a home.
- Remove, then keep checking.Submit removals and recheck on a schedule, because listings return.
- Tie it to physical security.If the address has been public for years, assume it is known and plan the residence’s protection accordingly.
That last point is the one people skip. Removal lowers the odds that a new person finds the address. It does nothing about the people who already have it. That is where a residential security assessment and protective intelligence come in.
How Delta handles it
Delta Strategic Solutions operates as a cyber-physical security company. We don’t separate the address that leaked online from the driveway it leads to. From our New York office in Uniondale, we support executives and families across Manhattan, Long Island and Westchester, and we work with clients in Florida and other high-demand markets across the U.S.
Every executive protection program we build starts with intelligence gathering and a review of the principal’s digital footprint, so the protection plan reflects what an adversary can actually see. When exposure turns into an active threat, our investigators and digital forensics team can trace where it came from.