AI Risk Management in Cybersecurity: Where the Risks Sit and How to Govern Them
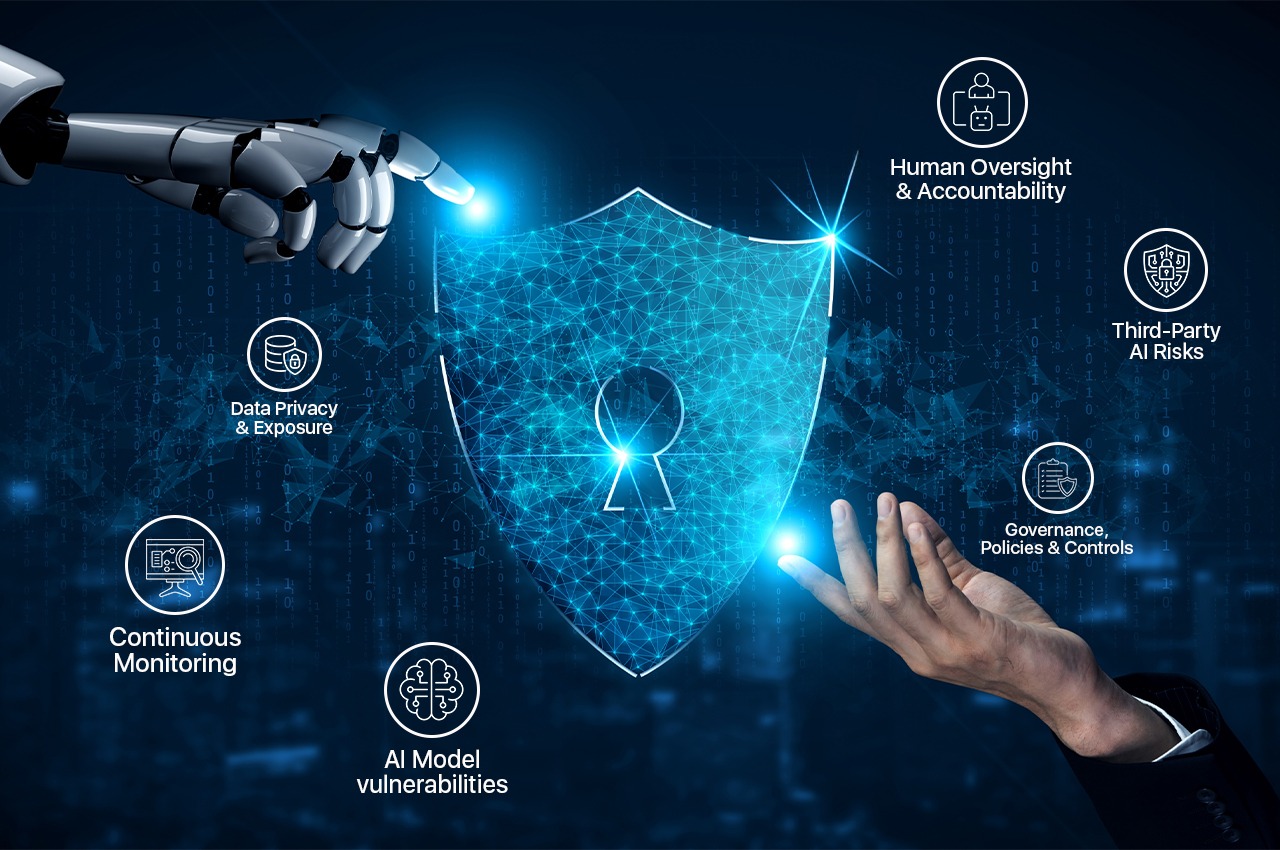
Artificial intelligence has changed what a security team has to watch. It writes the phishing email, clones the voice on the phone, and sorts the alerts that come back in. It also sits inside your own business, in the tools staff open every morning. Dealing with all of that is what AI risk management in cybersecurity is about: knowing where AI adds exposure, where attackers use it, and which rules keep your organization in control.
This guide is written for US business leaders, security managers and risk teams who want a clear picture rather than a product pitch. It covers where the risks sit, why they rarely stay inside the network, and a practical way to govern them.
What the term covers
The phrase gets used loosely, so it helps to split it into three separate jobs.
The first is the risk of the AI you adopt: chatbots, copilots, analytics tools, and vendor platforms that touch company data. The second is the risk of AI that others point at you, such as automated phishing or synthetic voice calls. The third is the use of AI as a defensive tool, for example to flag unusual log-in behavior or sift through large volumes of alerts.
Most organizations focus on the third and neglect the first two. A risk program has to hold all three in view, because a gap in anyone can undo the value of the others.
Where AI creates new exposure inside your own business
The quietest risks are often the ones staff create with good intentions.
Data leaving through prompts
An employee pastes a contract, a client list, or a draft board memo into a public AI tool to save time. Once it is submitted, the company may have little control over where that text is stored or reused.
Unvetted tools and plug-ins
Browser extensions and add-nos that promise to summarize meetings or write email often request broad access to inboxes, calendars and files. Each one is a new third party holding sensitive material.
Over-trusted output
AI systems can produce confident answers that are wrong. If an automated recommendation feeds a security or financial decision with no human check, one bad output can become a business error.
Manipulated inputs
Prompt injection is a technique where hidden instructions inside a document or web page steer an AI tool into doing something its user never intended, such as revealing data or acting. Any tool that reads outside content and has access to internal systems deserves extra scrutiny.
None of these means avoiding AI. It means knowing which tools are in use, what data they can reach, and who is accountable for them.
How attackers put AI to work against organizations
AI lowers the effort an attacker needs. Phishing messages no longer carry the clumsy grammar that once gave them away, and they can be tailored to a specific person in minutes using public information. A message that mentions a real project, a real colleague, and the right tone is much harder to dismiss.
Voice and video are the sharper edge. With a short audio sample, a criminal can imitate a senior leader on a call and ask finance to move money or share credentials. Our guide to deepfake fraud prevention for executives covers that scenario in detail.
Attackers also use AI for reconnaissance. Scraping social media, data broker listings and corporate pages to build a profile of an executive, a facility or a travel pattern used to take days. Automation shortens it, which means the window between exposure and exploitation is shrinking.
Why a cyber incident rarely stays digital
A breach of an email account or an assistant’s calendar is not only an IT problem. Those systems hold travel plans, meeting locations, building access details, and the routines of senior people. In the wrong hands, that information supports stalking, intrusion or targeted harassment as easily as it supports fraud.
This is why risk teams are starting to treat digital and physical exposure as one picture. A leader’s home address in a data broker file, a visitor list in a compromised system and a badge-access log in a poorly secured platform are the same kind of weakness viewed from different sides. Approaches built around cyber-physical risk integration look at both together, so a decision about an AI tool or data source also considers what it could reveal about people and places.
In practice, that means asking a simple question of every new AI deployment: if this system were compromised or misused, what could someone learn about our people, our sites or our schedules?
A practical way to govern it
A workable program does not need to be elaborate. Most organizations can make real progress with six habits.
Take inventory
List every AI tool in use, including the ones staff adopted on their own. You cannot manage what you have not found.
Write a short acceptable-use policy
Say plainly what may and may not be entered into AI tools, with clear examples such as client data, legal documents and credentials.
Vet vendors before they connect
Ask what data a tool can access, where it is stored, who can see it, and what happens when the contract ends.
Keep a person in the loop
Any AI output that triggers a payment, a lock-out, a disciplinary step or a security response should have a named human who reviews it.
Log and monitor
Record which systems AI tools reach and review that activity, so an unusual pattern is noticed early.
Rehearse
Run a tabletop exercise on a scenario such as a cloned executive voice requesting an urgent transfer, and include finance, communications and security in the room.
Then revisit the list regularly. AI tools change quickly, and a policy written once and filed away will drift out of date within a few months.
The takeaway
AI is now part of how organizations work and how they are attacked. The sound response is neither fear nor blind adoption. It is a clear inventory, simple rules, human review where the stakes are high, and a habit of asking what a system could reveal about the people and places it touches.